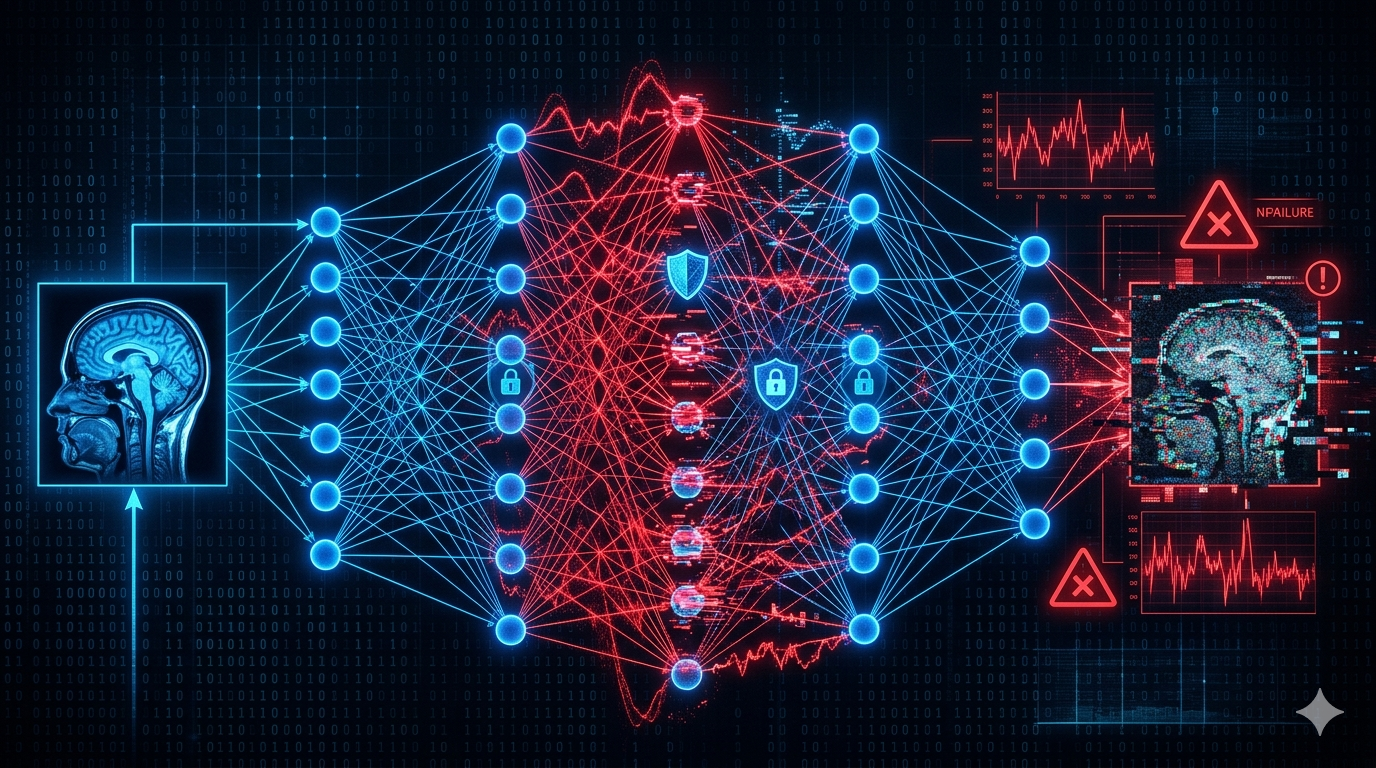
Headline result: Robustness across security, health, and social systems
AI systems deployed in healthcare, security, and finance can be manipulated by adversarial inputs — carefully crafted perturbations that cause confident wrong predictions. We develop defenses, detection systems, and robust architectures that remain reliable even when attacked.
Research Areas
- Adversarial CAPTCHAs & Usable Security — Designing CAPTCHAs that are easy for humans but hard for AI using precise noise targeting. Published at AAMAS 2026.
- Encrypted Network Traffic — Detecting anomalies and classifying malicious traffic in fully encrypted streams without decryption, using contrastive learning for zero-day attacks.
- Android Malware Detection — ML-based classifiers hardened against evasion attacks, maintaining accuracy even when adversaries know the detection method.
- Healthcare AI Robustness — Adversarial training and certified defenses for medical diagnosis and patient prediction models under attack.
- Social Network Manipulation — Detecting coordinated inauthentic behavior, bot accounts, and disinformation using graph-based anomaly detection.
Technical Approaches
- Contrastive & Self-Supervised Learning — SimCSE-based methods that build robust representations effective for zero-shot detection of novel attack patterns.
- Adversarial Training & Certified Defenses — Training on adversarial examples with provable robustness guarantees via randomized smoothing for safety-critical applications.
- Privacy-Preserving Detection — Federated learning and differential privacy techniques that protect sensitive data while maintaining detection performance.
Key publications & resources
- Publications — filter by the Cybersecurity topic to see this project's papers.
- Code & software — lab repositories, datasets, and tools.
Collaborate with us
We welcome academic and industry collaborations, and motivated graduate students, on this research line. Get in touch →